An email verifier is a tool that checks whether an email address is real and able to receive mail — before you send anything to it. That’s the short answer. The longer, more useful answer is what it actually does under the hood, because “verified” isn’t one check. It’s four or five, stacked, each one catching a different kind of failure the others miss.
If you’ve ever wondered why a tool flags one address as “valid,” another as “risky,” and a third as “invalid” when they all look equally normal to your eye, this is why. Each label comes from a different layer of checking, and understanding the layers tells you how much to trust the result — and, just as importantly, what a given result doesn’t tell you.
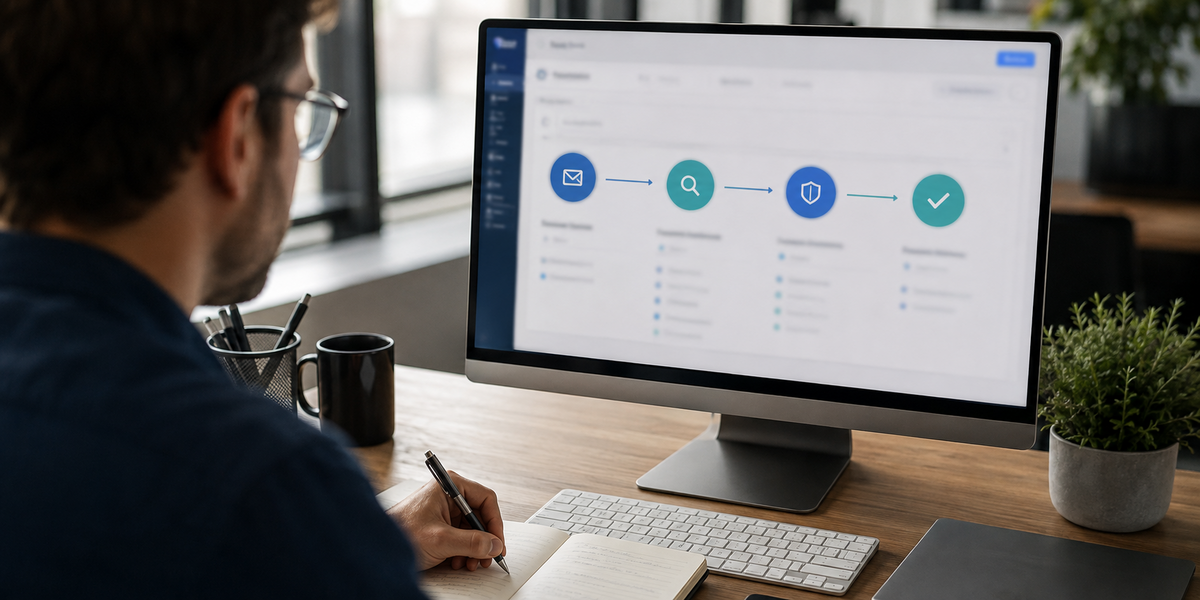
The four layers of a real verification
Layer 1: Syntax check
This is pattern-matching. Does the address have exactly one @, a domain with a dot in it, no illegal characters? It’s instant and it catches typos — “john@gmial.com” fails here immediately.
It’s also the weakest layer on its own. A syntactically perfect address can still be completely dead. This step just clears out the obvious junk before the tool spends more effort on the rest. Think of it as the cheapest possible filter — a computer can check a million addresses for syntax in the time it takes to check a handful with the deeper layers, so it makes sense to run this one first and only pass the survivors along.
Syntax rules follow a formal specification (RFC 5322, if you want to look up the actual standard), and while most everyday addresses are simple, the spec technically allows some surprising things — quoted strings, certain special characters in the local part — that a naive regex might reject even though they’re valid. A well-built syntax checker accounts for this, rather than rejecting anything that doesn’t match the most common, simplified pattern.
Layer 2: Domain and MX record check
Next, the verifier looks up whether the domain even has a mail server willing to accept messages — its MX (Mail Exchange) record. No MX record means the domain can’t receive email at all, full stop, regardless of what’s typed before the @.
This catches a specific and common failure mode: someone typos a company domain, or types an address at a domain that used to exist but doesn’t anymore. Public sources like IANA’s registry documentation explain how domain and DNS records work if you want the technical background. It’s also worth knowing that a domain having a working website doesn’t guarantee it has working email — the two are handled by separate DNS records (A records for the website, MX records for mail), and it’s entirely possible, more common than you’d think, for a domain to serve a live website while its mail service has lapsed or was never set up in the first place.
Layer 3: SMTP mailbox check
This is the layer that actually asks the mail server about the specific mailbox, not just the domain. The verifier connects to the server and steps through part of the SMTP protocol — the same handshake a real mail server does — up to the point where it would ask “does this specific mailbox exist,” then stops before sending an actual message.
The server’s response tells the tool whether the mailbox accepts mail, rejects it outright, or gives an ambiguous answer. That ambiguous case is common enough that it deserves its own layer, and it happens for a few distinct reasons: the receiving server might be temporarily overloaded and issue a soft, retry-later response (a 4xx code in SMTP terms); it might practice greylisting, deliberately stalling unfamiliar senders on the first attempt to filter out spam-sending scripts that don’t retry; or it might simply not implement a clear accept/reject distinction at this protocol layer at all, which some large providers do intentionally as an anti-abuse measure.
Layer 4: Catch-all and disposable detection
Some domains are configured to accept mail sent to any address at that domain, valid or not — these are “catch-all” domains. When a verifier hits one, the SMTP check in Layer 3 can’t tell you anything useful about the specific mailbox, because the domain says yes to everything, real mailbox or not.
A good verifier flags this explicitly instead of guessing, which matters because silently treating a catch-all response as “confirmed valid” would be actively misleading — it would tell you an address is real when the honest answer is “unknown.” It also checks the domain against known disposable/temporary email providers (Mailinator and similar services people use to avoid giving a real address). Both of these get their own explainer in our guide to spotting fake, disposable, and catch-all addresses.
Why these layers have to run in this order
It’s not arbitrary that syntax comes first and SMTP comes last. Each layer is progressively more expensive to run — a syntax check is essentially free computationally, an MX lookup requires a DNS query but is still fast, and an SMTP handshake requires actually opening a network connection to a third-party mail server and waiting for a real response, which can take a meaningful fraction of a second or occasionally longer if the server is slow or the connection needs a retry.
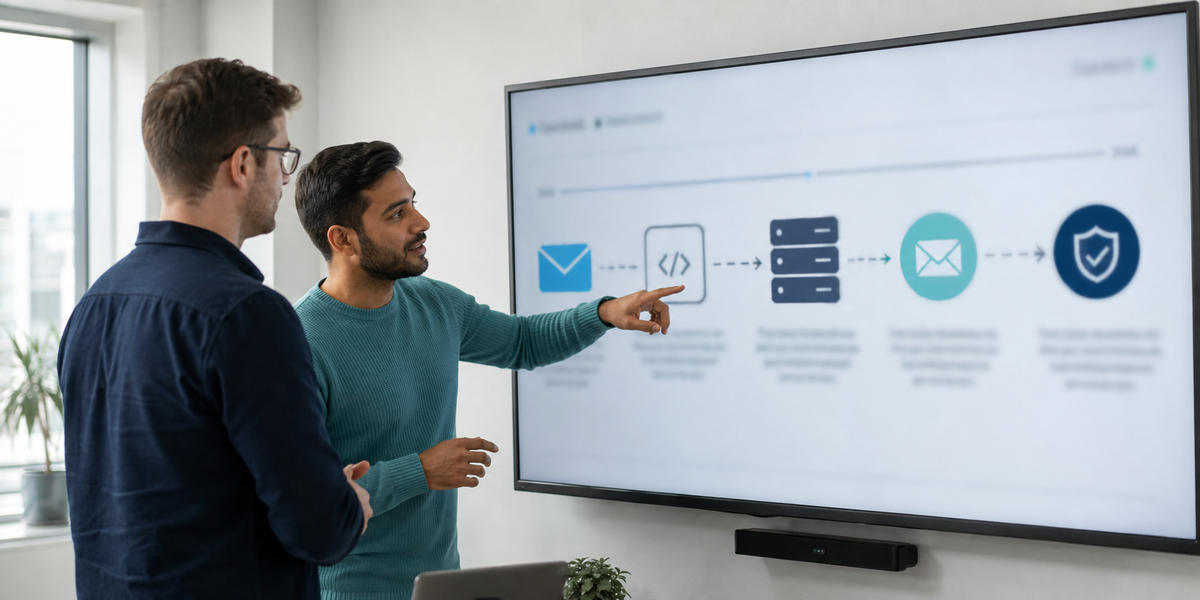
Running the checks in increasing order of cost means a tool doesn’t waste an SMTP handshake — the slowest, most resource-intensive step — on an address that already failed a syntax check that took a fraction of a millisecond. This ordering also matters for a subtler reason: repeatedly hitting a mail server with SMTP handshake requests, especially at volume, is exactly the kind of pattern that server’s own anti-abuse systems are watching for. A verification tool that’s smart about only escalating to Layer 3 and 4 when the address has already passed Layers 1 and 2 is, among other things, being a better citizen of the mail ecosystem it’s checking against.
How sfemailverifier.com runs these checks
Paste an address into the checker on the homepage and it runs all four layers in a few seconds — no signup, no email sent to the address itself. You get back one of a handful of statuses (valid, invalid, risky, catch-all, disposable), which we define in plain terms in what “email verified” actually means.
For more than one address at a time, the bulk verifier runs the same four layers across an uploaded CSV, which matters if you’re cleaning a signup list or a CRM export rather than checking one address by hand. And for anyone building verification directly into a signup flow or backend pipeline, the developer API exposes the same checks programmatically — see our API integration guide for working code examples in a few languages.
A real example of why the layers matter
Imagine a small B2B software company — call it Ledgerly — running a webinar signup form. Of 600 registrants, a syntax check alone would clear about 580 as “fine.” But run the full four-layer check and a different picture shows up: 40 addresses have no MX record (dead domains), another 25 sit behind a catch-all domain and can’t be confirmed either way, and 8 are disposable addresses from people who didn’t want to give a real one.
That’s 73 addresses — over 12% of the list — that a syntax-only check would have missed entirely. Ledgerly’s marketing team would have mailed all of them, taken the bounce hit, and had no idea why their sender reputation dipped the following week. Worse, without the layer breakdown, they’d have no way to distinguish “this address is definitely dead” (the 40 no-MX cases, worth removing outright) from “this address is genuinely uncertain” (the 25 catch-all cases, which might well include real, reachable people whose company just runs a permissive mail server). Lumping all 73 into one undifferentiated “bad” bucket would have meant either sending to addresses that were going to bounce, or discarding real leads out of an abundance of caution that wasn’t actually necessary.
What each layer specifically can’t tell you
It’s worth being direct about the limits of each layer, because overselling any one of them is how trust gets lost.
Syntax checking can’t tell you anything about deliverability. A perfectly formatted address at a domain with no mail server is still dead, and syntax checking alone has no way to know that.
MX record checks can’t tell you about a specific mailbox. A domain having a working mail server doesn’t mean every possible address at that domain corresponds to a real person’s inbox.
SMTP checks can be fooled by catch-all configurations, and can be blocked or delayed by greylisting even when the mailbox is completely real — which is why a single SMTP attempt without retry logic can produce a false negative.
Catch-all and disposable detection is a domain-level signal, not a mailbox-level one. It tells you the domain’s behavior, which affects how much you should trust (or distrust) the Layer 3 result for any address at that domain — it doesn’t independently confirm or deny a specific address.
How verification behaves differently across big providers
Not every mail server responds to these checks the same way, and it’s worth knowing the general patterns because they explain a lot of “why did this address come back ambiguous” questions.
Gmail and Google Workspace addresses are, in practice, some of the harder ones to get a clean SMTP-level signal from. Google’s mail infrastructure has moved toward accepting connections at the RCPT TO stage for a wider range of addresses than it used to, and sorting out deliverability through other means after that point — which means the Layer 3 check described above can come back less decisive for Gmail domains than it would have several years ago. This isn’t a flaw in any particular verifier. It’s a deliberate choice by a large provider about how much information to expose at the protocol level, generally framed around limiting what spammers can learn from probing addresses.
Microsoft-hosted domains (Outlook, Hotmail, and custom domains on Microsoft 365) tend to give clearer accept/reject signals at the SMTP layer, though behavior varies by the specific configuration a given organization has set up — some enterprise Microsoft 365 tenants use catch-all-style configurations for their own reasons, which produces the same ambiguous result described in Layer 4 above.
Smaller business domains, hosted through a huge range of providers, are the most variable of all. Some are strict and give clean, confident answers. Some are catch-all by default because nobody on staff ever changed the setting. There’s no universal rule here beyond “check and see,” which is exactly what the four-layer process is built to do.
Why some addresses take longer to verify than others
If you’ve ever noticed one address in a batch taking noticeably longer to return a result than the rest, there’s usually a specific reason, and it maps back to the layers above. A syntax failure returns instantly, because it never leaves your own system. An MX lookup that finds no record also returns fast, since a DNS query is quick even when the answer is “nothing here.” The slow cases are almost always ones that make it to Layer 3 and hit a mail server that’s slow to respond, temporarily overloaded, or practicing greylisting — a deliberate stall-and-retry pattern some servers use specifically to filter out spam senders that don’t bother retrying a failed connection.
A well-built verifier handles this by retrying rather than giving up after one attempt and reporting a false invalid. That retry logic is invisible to you as the end user, but it’s part of why bulk jobs occasionally take a few minutes rather than resolving instantly for every single row — some rows are doing more real work behind the scenes than others.
Is a “verified” address a guarantee?
No, and any tool that claims otherwise is overselling. Even a full four-layer check can’t guarantee delivery. A mailbox can be verified as valid on Tuesday and get deactivated by Thursday. Catch-all domains, by definition, can’t be resolved to a certain yes or no at the individual mailbox level — that’s a limitation of how those domains work, not a gap in the checking.
What verification does is cut your risk down close to zero instead of leaving it at whatever your raw, unchecked list started at. That’s a meaningfully different thing than “will never bounce,” and worth being honest about. Anyone selling verification as a 100% guarantee against bounces is either not being straight with you, or doesn’t fully understand what the underlying protocol can and can’t confirm.
How to sanity-check a verifier’s results yourself
You don’t have to take any tool’s word for it blindly. A few quick spot-checks build confidence in a given result, especially for addresses you’re unsure about:
Check a known-good address. Run your own email through the checker. If it doesn’t come back valid, something’s off with the tool, not with your inbox.
Check an obviously fake one. Try “notarealaddress@notarealdomain12345.com” and confirm it comes back invalid. A tool that can’t catch this isn’t doing basic MX-layer checking.
Compare a “risky” or “catch-all” result against what you know about the domain. If a small business contact comes back catch-all, a quick look at their company website (does it look like a real, operating business?) tells you more about how much to trust that specific address than the status alone can.
None of this replaces the actual checks — it’s just a way to build intuition for what each status means in practice, which makes the results more useful once you’re looking at hundreds of them in a bulk list rather than one at a time.
See what your addresses actually check out as
Paste an email into the free checker on the sfemailverifier.com homepage and see which layer flags it, if any. For a full list, the bulk verifier and the developer API run the same checks at scale.
Questions
Frequently asked questions
What does an email verifier actually check?
Generally, an email verifier checks four core things: whether the address is correctly formatted, whether the domain has a working mail server, whether the specific mailbox appears to accept mail, and whether the domain is catch-all or associated with disposable email services. Different tools may implement these checks differently, but these are the main layers.
Does verifying an email send a message to it?
No. A proper verifier performs an SMTP conversation but stops before actually sending a message. The mailbox owner doesn’t receive an email during the verification process.
How accurate is email verification?
Verification can be highly accurate for domains with functioning MX records and non-catch-all mailboxes, often reaching 95%+ accuracy in those conditions. Accuracy is inherently less conclusive for catch-all domains because the mail server accepts messages for addresses regardless of whether a specific mailbox exists.
Can a verified email still bounce?
Yes. An email address can become invalid after it was verified for example, if the mailbox is closed, deactivated, or becomes full. Verification reflects the mailbox’s status at the time of the check, not a permanent guarantee of future delivery.
Is email verification the same as email validation?
The terms are often used interchangeably, but technically they can refer to different levels of checking. Validation may mean only checking whether the email syntax is valid, while verification generally implies deeper checks such as MX, SMTP, and catch-all detection. When evaluating a tool, check which verification layers it actually performs rather than relying on the terminology.
Why can an SMTP check take longer than other verification layers?
SMTP verification requires a live network connection to the recipient’s mail server and a response from that server. Syntax checking happens locally and an MX check is typically a quick DNS lookup. Mail servers can also respond slowly or temporarily delay connections through mechanisms such as greylisting, which can make SMTP checks take longer.
Do all email verification tools check the same four layers?
No. Some free or basic tools may only perform syntax and MX checks without conducting deeper SMTP or catch-all analysis. That’s why the term “verified” can mean different things across different providers.
What happens if a mail server doesn’t respond during an SMTP check?
A well-designed verifier should retry rather than immediately marking the address invalid. A lack of response may be caused by a temporary server problem, connection delay, or greylisting rather than an actual rejection.
Why can Gmail addresses sometimes be less conclusive than other domains?
Google’s mail infrastructure may accept SMTP connections for a broader range of addresses and use other mechanisms to determine final deliverability. This is an anti-abuse approach and can make SMTP-level verification less definitive for some Gmail addresses.
Should I trust a verifier that only checks syntax and calls it “verified”?
Be cautious. Syntax checking is useful and fast, but it only confirms that an address follows the expected format. Calling that result “verified” without deeper MX, SMTP, and catch-all checks can give a misleading impression of what was actually confirmed.
Is there a difference between verifying an email and validating it at signup?
In everyday usage, the terms often mean the same thing. Technically, validation can refer to syntax checking, while verification generally suggests a broader examination of the domain, mailbox, and catch-all status. The important question is which checks the tool actually performs, regardless of the terminology it uses.